🛡️ Governance & Risk Management
Build stronger security programs through governance frameworks, risk assessments and strategic cybersecurity planning.
Helping Businesses Reduce Risk,
Improve Compliance & Build Cyber Resilience
 Cyber Security Consulting • Kothrud Pune
Helping businesses strengthen cybersecurity, reduce risks, improve compliance readiness, and build a resilient security culture through practical consulting and awareness programs.
ISO 27001 • DPDPA • Risk Assessments • Virtual CISO • Security Awareness Training
A practical cybersecurity consulting partner helping organizations improve security governance, compliance readiness, risk management, and employee awareness.
Build stronger security programs through risk assessments, governance frameworks, and strategic cybersecurity planning.
Support for ISO 27001, DPDPA, security controls, audit preparation, and regulatory compliance initiatives.
Employee awareness sessions, phishing simulations, and practical training to reduce human cyber risks.
Executive-level cybersecurity guidance for organizations that need strategic security leadership without a full-time CISO.
Helping businesses strengthen cybersecurity, reduce risks, improve compliance readiness, and build a resilient security culture through practical consulting, governance programs, awareness initiatives, and strategic security advisory services.
A trusted cybersecurity consulting partner helping organizations improve security posture, strengthen compliance readiness, and reduce cyber risks through practical solutions.
Build stronger security programs through governance frameworks, risk assessments and strategic cybersecurity planning.
Support for ISO 27001, DPDPA, audit preparation, security controls and compliance initiatives.
Employee awareness sessions and phishing simulations that help reduce human cyber risks.
Executive-level cybersecurity guidance without the cost of a full-time CISO.
Helping organizations strengthen security posture through practical consulting, compliance support, risk management, awareness programs, and executive cybersecurity guidance.
Guidance for ISO 27001 implementation, readiness assessments, audit preparation, and information security management systems.
Support organizations in understanding privacy obligations, identifying gaps, and improving data protection practices.
Identify vulnerabilities, assess cyber risks, and develop practical strategies to strengthen organizational resilience.
Build a stronger security culture through awareness programs, phishing simulations, and employee education initiatives.
Executive-level cybersecurity leadership and strategic guidance without the need for a full-time CISO.
Strengthen governance frameworks, improve compliance readiness, and align security initiatives with business goals.
Helping businesses across diverse industries strengthen cybersecurity, improve compliance readiness, and reduce operational risks.
Cybersecurity governance, awareness programs, risk assessments, and compliance support for technology-driven businesses.
Protect patient information, strengthen privacy controls, and improve compliance readiness.
Support cyber risk management, governance initiatives, and regulatory compliance requirements.
Improve resilience against operational disruptions, cyber threats, and security vulnerabilities.
Build strong security foundations early and scale confidently with practical cybersecurity guidance.
Protect business data, client information, and critical operational processes.
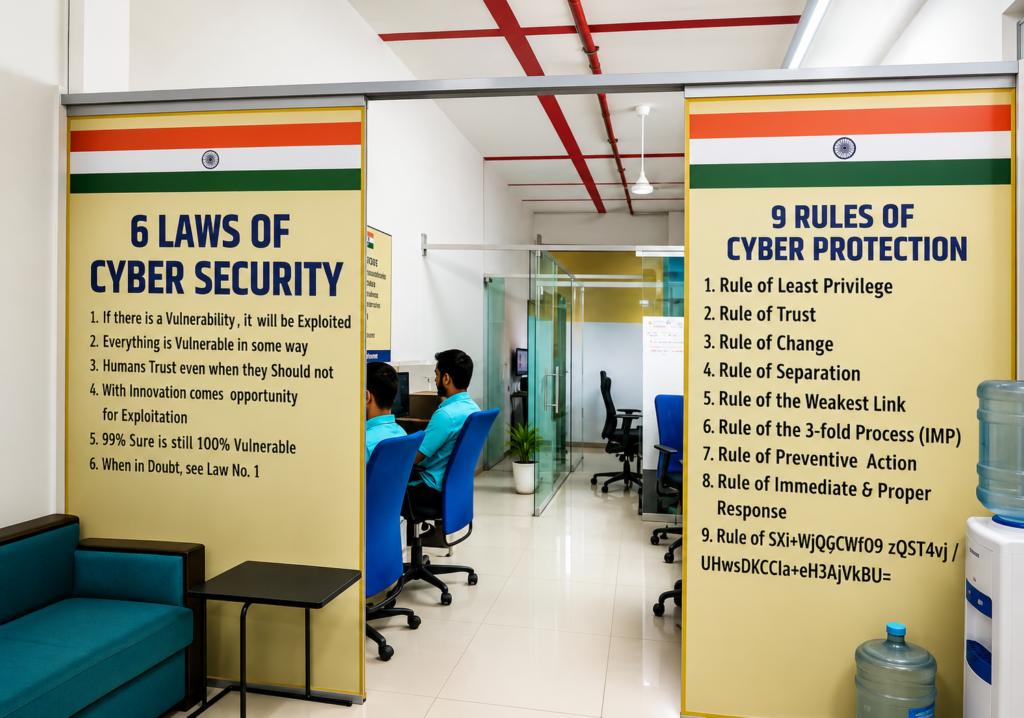
Helping businesses build stronger security foundations, improve governance practices, and prepare for evolving cyber risks with confidence.
Supporting organizations across globally recognized frameworks, privacy requirements, security controls, and governance initiatives.
A structured cybersecurity and compliance program helps organizations improve operational resilience, strengthen stakeholder trust, manage risks proactively, and prepare for evolving regulatory expectations.
Practical cybersecurity guidance designed to help organizations strengthen security posture, improve compliance readiness, and manage cyber risks effectively.
Organizations choose SAARTH INFOSEC for practical cybersecurity expertise, regulatory knowledge, and a business-focused approach that delivers measurable security improvements.
Answers to some common questions about cybersecurity consulting, compliance readiness, governance, and risk management services.
SAARTH INFOSEC supports organizations through cybersecurity consulting, risk assessments, governance advisory, compliance readiness programs, Virtual CISO services, and security awareness initiatives.
Cybersecurity consulting helps businesses identify risks, strengthen security controls, improve resilience, support compliance efforts, and build greater confidence among customers and stakeholders.
Yes. Our team helps organizations improve governance practices, prepare for audits, implement security controls, and align with relevant compliance requirements.
Absolutely. Security risks affect organizations of all sizes. Practical cybersecurity guidance helps growing businesses protect critical assets and prepare for future challenges.
You can reach our team through phone, WhatsApp, website inquiries, or by scheduling a consultation with one of our cybersecurity specialists.
Whether you need ISO 27001 guidance, DPDPA compliance support, cybersecurity awareness training, risk assessments, or strategic security consulting, our team is ready to help your organization reduce risk and improve resilience.